
Scope
Applies to controllers in Thailand and to controllers abroad that offer goods or services to, or monitor the behaviour of, people in Thailand.
Thailand's Personal Data Protection Act 2019 has applied fully since 1 June 2022. Organisations need a lawful basis, a privacy notice, records of processing, and must notify the PDPC of risky breaches within 72 hours.
Thailand's Personal Data Protection Act 2019 has applied fully since 1 June 2022. Organisations need a lawful basis, a privacy notice, records of processing, and must notify the PDPC of risky breaches within 72 hours.
This page summarises a PDPA readiness checklist for Thai companies and foreign companies processing data of people in Thailand. General information under Thai law; not legal advice on your situation and no outcome is promised.
Applies to controllers in Thailand and to controllers abroad that offer goods or services to, or monitor the behaviour of, people in Thailand.
Identify a basis such as contract, legal obligation, legitimate interest or consent; sensitive data needs explicit consent unless an exception applies.
Privacy notice, record of processing activities, data processing agreements with vendors, and a data-subject request procedure.
Certain organisations must appoint a DPO under PDPC criteria, such as large-scale or sensitive-data processing as a core activity.
The destination must have adequate standards or appropriate safeguards under PDPC notifications.
Notify the PDPC within 72 hours where a breach risks rights and freedoms. Statutory administrative fines reach up to THB 5 million, plus civil and criminal liability.
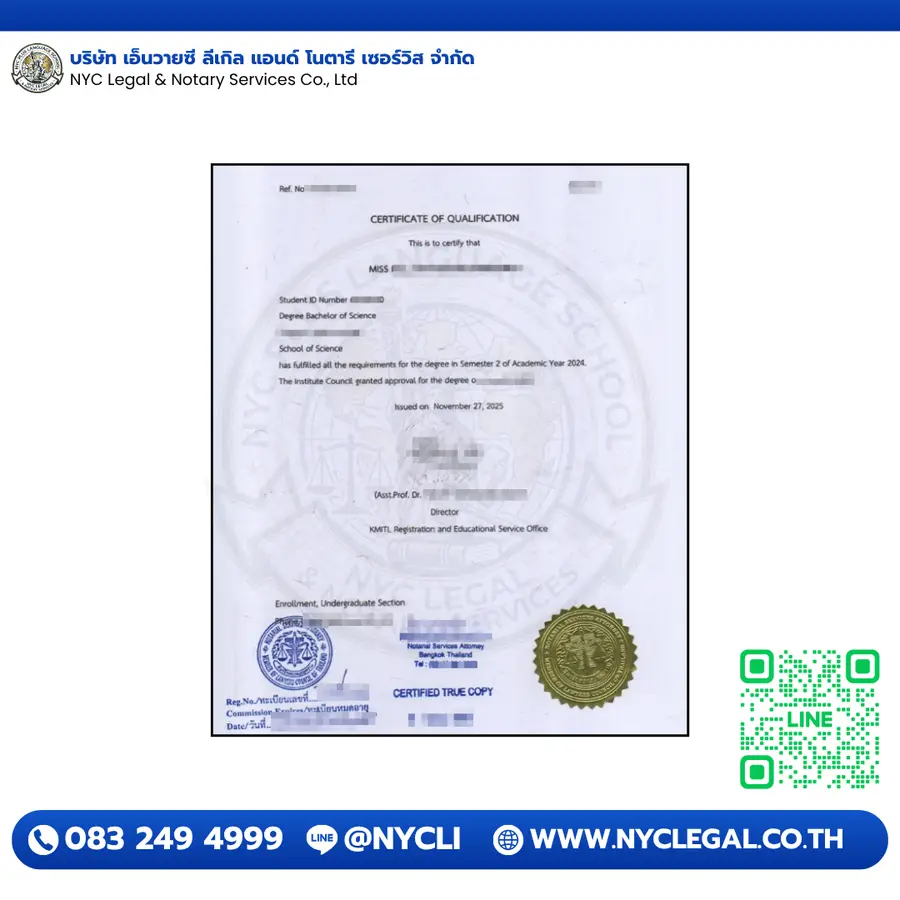
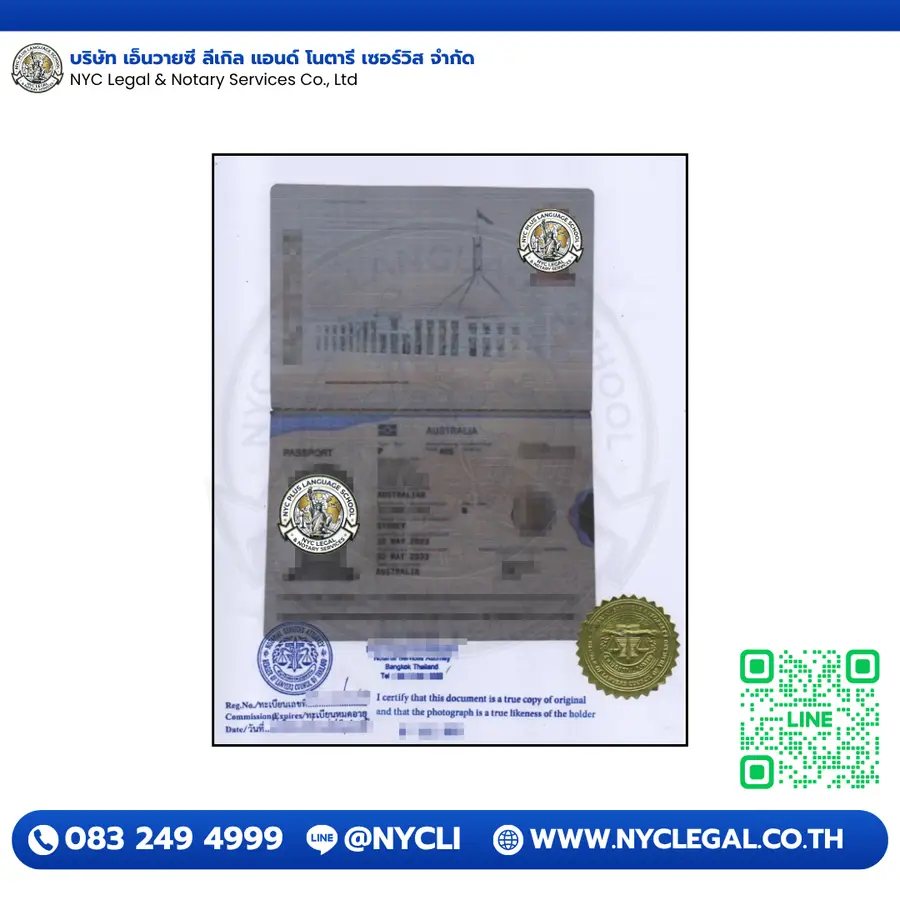
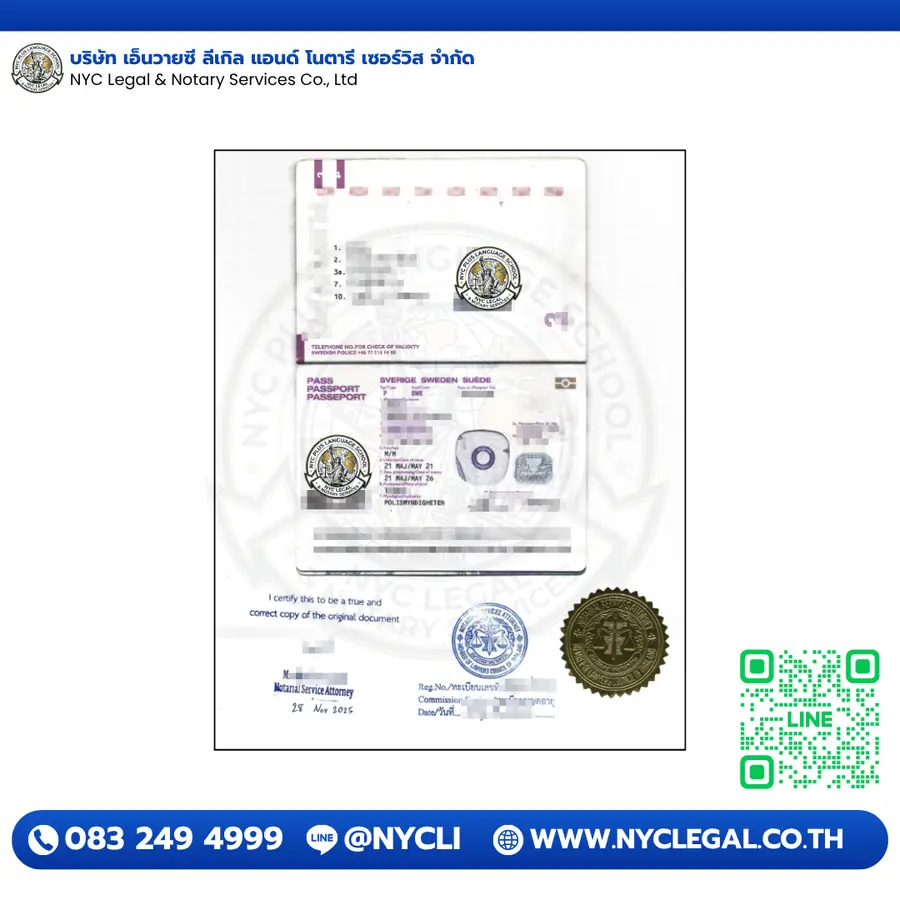
Full coverage
Documents accepted nationwide
Ask our team; confirmed in writing before work starts
Most clients pair these services together
Fees and turnaround depend on the document type and receiving authority — please contact our staff by phone, LINE or email.